The global population of connected devices surpassed 21 billion at the end of 2025 and is on a trajectory to approach 39 billion by the year 2030. For hardware developers and engineers, getting a microcontroller online to transmit sensor data is an exciting and essential milestone. Edge computing now powers everything from smart agriculture to industrial automation. However, the gap between building a successful breadboard prototype and deploying a secure edge ecosystem is vast. Automated attacks targeting internet-connected hardware have escalated rapidly, reaching an average of 820,000 malicious hacking attempts daily. Securing these network endpoints is no longer an optional feature. It is a critical requirement for any modern engineering project, demanding rigorous attention from the initial design phase through to final deployment.
Transitioning from Prototyping to Enterprise Deployment
While deploying a basic connected device, such as a NodeMCU IoT environment monitor, is often the first step in a hardware prototype, securing the data it transmits requires an enterprise-level approach. Engineers must recognise that the same features making these devices accessible for development also make them attractive targets for malicious actors.
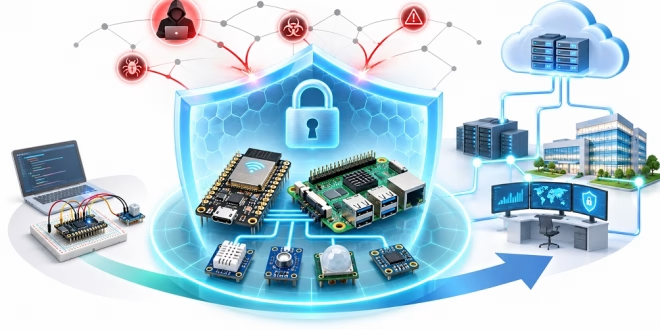
When environmental sensors or industrial microcontrollers are connected to broader corporate networks, they become potential entry points for cybercriminals. Modern eCrime breakout times (the critical window from an attacker gaining initial access via an edge device to moving laterally across a network) have plummeted to just 29 minutes. If a vulnerability in an ESP32 or Raspberry Pi is exploited, attackers can pivot into centralised servers before network administrators even realise a breach is underway. The threat is not just theoretical. In late 2025, a massive distributed denial-of-service attack was launched by the Aisuru botnet, which successfully hijacked over 500,000 poorly secured edge devices globally to orchestrate severe network disruptions.
Why Edge Endpoints Demand Proactive Defence
Because microcontrollers often lack the memory and processing power to run traditional endpoint security agents, modern organisations must increasingly rely on dedicated Data breach readiness software to monitor their vast data landscapes and instantly detect anomalous activity. Implementing such solutions allows companies to identify unusual traffic patterns originating from seemingly innocuous hardware, thereby neutralising threats before they escalate into catastrophic network compromises.
The stakes for enterprise data ecosystems are incredibly high. A severe IoT data breach involving connected hardware from Mars Hydro recently exposed 2.7 billion records via an unsecured cloud database. This leak included Wi-Fi network credentials and device configurations that could grant attackers direct local network access. Similarly, the high-profile breach of internet-connected security cameras from Verkada serves as a foundational industry case study. It demonstrated exactly how compromising physical edge devices can directly expose highly sensitive internal operations. With approximately 98% of all IoT device traffic currently transmitted unencrypted, bad actors can easily intercept critical network commands and credentials if a single hardware endpoint is compromised.
Meeting New Australian Security Standards
In Australia, the regulatory landscape is rapidly shifting to enforce stronger hardware security at the manufacturing level. The Australian Signals Directorate reported a 20% increase in cybersecurity incidents during the 2025 to 2026 financial year, responding to over 1,500 major events. To combat this escalating threat, the Cyber Security (Security Standards for Smart Devices) Rules 2025 now legally mandate baseline cybersecurity requirements for most smart devices acquired in the country.
Under these new regulations, engineers must ensure their connected hardware adheres to three core rules:
A strict ban on universal default passwords across all manufactured hardware to prevent trivial automated exploits.
Mandatory vulnerability reporting mechanisms to allow independent researchers to disclose flaws securely and efficiently.
Transparent minimum security update periods clearly communicated to buyers at the point of sale, ensuring long-term device integrity.
Furthermore, a government-backed Cybersecurity Labelling Scheme is being implemented across Australia. This initiative helps enterprise buyers easily compare device security before integrating third-party sensors into their networks. The Australian Cyber Security Centre actively advises developers to follow its IoT Secure-by-Design Guidance, which outlines 13 fundamental principles to secure edge technologies before they reach production. Adhering to these guidelines not only ensures compliance but also builds critical trust with enterprise clients who are increasingly wary of hardware vulnerabilities.
The Financial and Operational Stakes
The financial fallout from poorly secured IoT infrastructure can cripple an organisation. According to IBM's Cost of a Data Breach Report 2026, the global average cost of a data breach saw a 12% increase over the previous year. These costs reached record highs due to longer escalation times and advanced AI-enabled malware designed specifically to exploit fragmented edge networks.
This economic impact aligns with recent research indicating that IoT-targeted malware attacks surged by 124% year-over-year. Cybercriminals are increasingly weaponising connected edge networks for physical extortion, leading to a nearly 50% surge in targeted ransomware campaigns directed at industrial and operational technology sensors. As the lines between hardware engineering and enterprise IT continue to blur, developers must adopt secure architectures from the ground up. By implementing proper encryption libraries, disabling unnecessary debugging ports, and preparing robust incident response strategies, the hardware community can help prevent the next catastrophic network intrusion and safeguard the future of connected infrastructure.